EU-hosted, GDPR by default, and your data stays yours.
ZeePMT is built for public-sector environments where compliance, transparency and accountability are essential — where being able to say plainly where your data lives, who can see it, and who owns it is part of earning the right to hold it.
Controls built into how operations run
Most of these controls follow from running operations properly. Role-based access is also data minimisation; audit logs are every action recorded in the system.
100% European hosting
Your data is held within the EU, under a single, well-understood regulatory regime — a condition many EU-funded programmes and public institutions require, not a nice-to-have.
GDPR-aligned by default
Data protection and access control are built in, not bolted on: lawful processing, data minimisation, and user anonymisation for sensitive records.
You own your data
You are the data controller and retain ownership of your data. The provider is contractually restricted from re-using it — including for AI-model training — and it is never pooled across clients.
Role-based access control
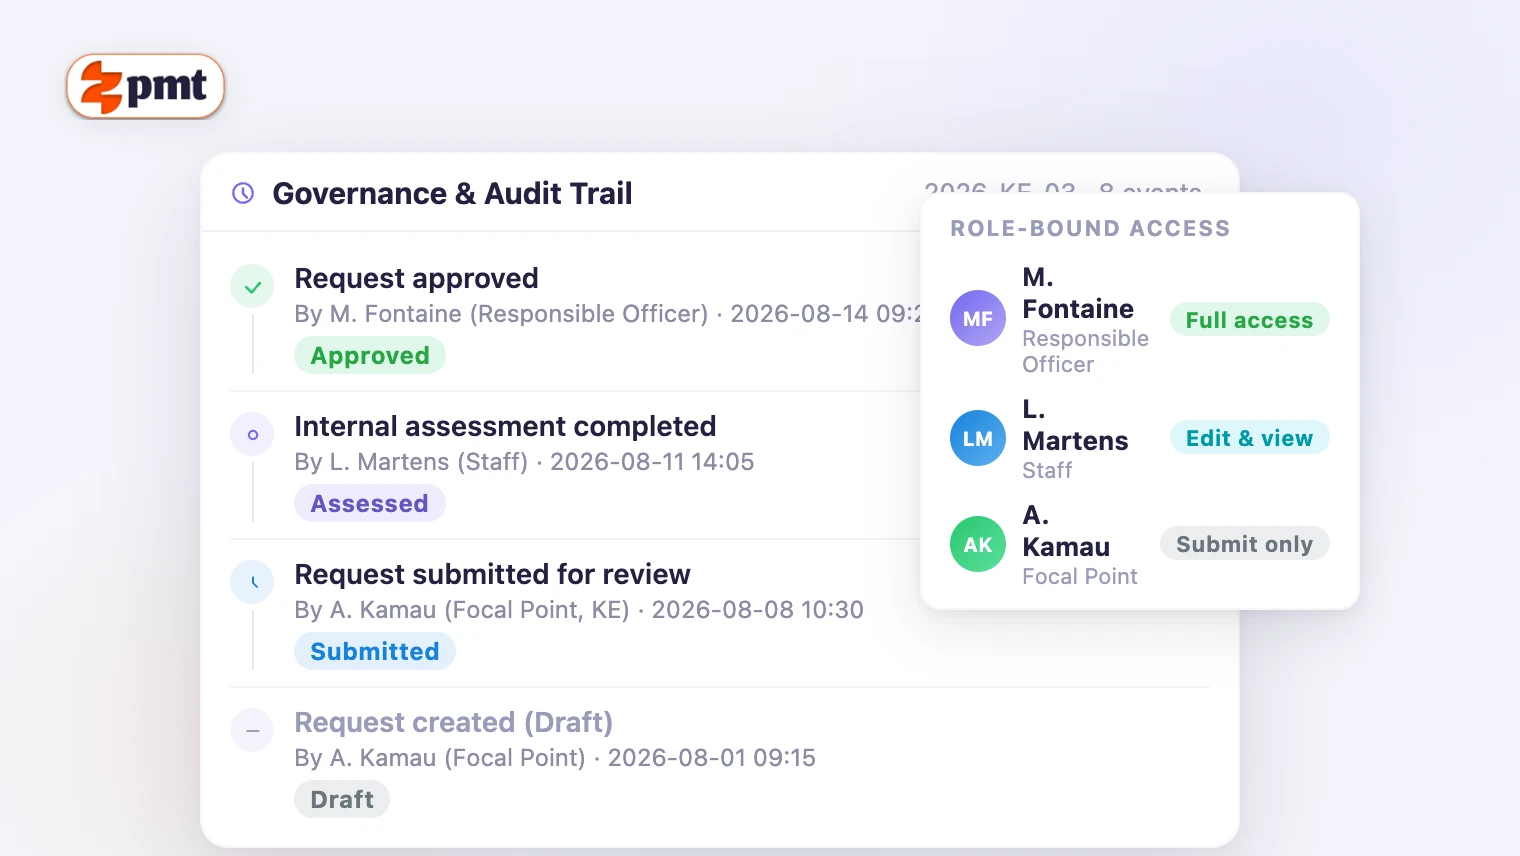
Who may create a record, who validates it, and who is merely informed is enforced by the system itself — the accountability structure a donor or institutional review expects.
Audit-grade traceability
Structured audit logs and version control mean every operational, financial or results figure can be traced back to the specific unit, role and date that produced it.
Two-factor authentication & access logging
Configurable authentication, automated notifications and access logging keep sensitive operational data protected and accountable.
Data ownership is a material trust signal for public-sector clients
Because you remain the data controller and your data is kept separate and never pooled, sensitive information about your experts, partner institutions and programmes stays under your control. It is a commitment you can present in a procurement review.
- You are the data controller.
- You retain ownership of your data.
- It is never re-used — including for AI-model training — without a separate agreement.
- It is never pooled across clients.
- It is held within the EU.
Every action logged, attributed and traceable.
ZeePMT's governance model is how the system works — not a separate compliance add-on. Role-based access, structured audit logs and version control mean every operational decision can be traced to the unit, role and date that made it.
Security and compliance documentation for your review process
Download the ZeePMT Procurement Support Pack — a single document covering the technical specification, GDPR and data-ownership terms, competitive justification for a negotiated procedure, and indicative pricing for budget planning.
The pack is written for procurement officers, steering committees and IT/security leads. It covers:
- Full functional and technical specification
- Data Processing Agreement (DPA) summary — GDPR Art. 28 compliant
- Hosting, security controls and certification status
- Data portability, export terms and source-code escrow option
- Competitive analysis versus alternative tools
- Justification for negotiated procedure / direct award
- Indicative pricing and 5-year total cost of ownership
Request the documentation
Leave your name, organisation and work email. We will send the Procurement Support Pack the same working day — no sales call required.
Compliance you can demonstrate, not just claim
We'll walk your IT, legal and compliance teams through hosting, data residency, access control and the data-ownership guarantee.